Connect
November 23–27, 2026
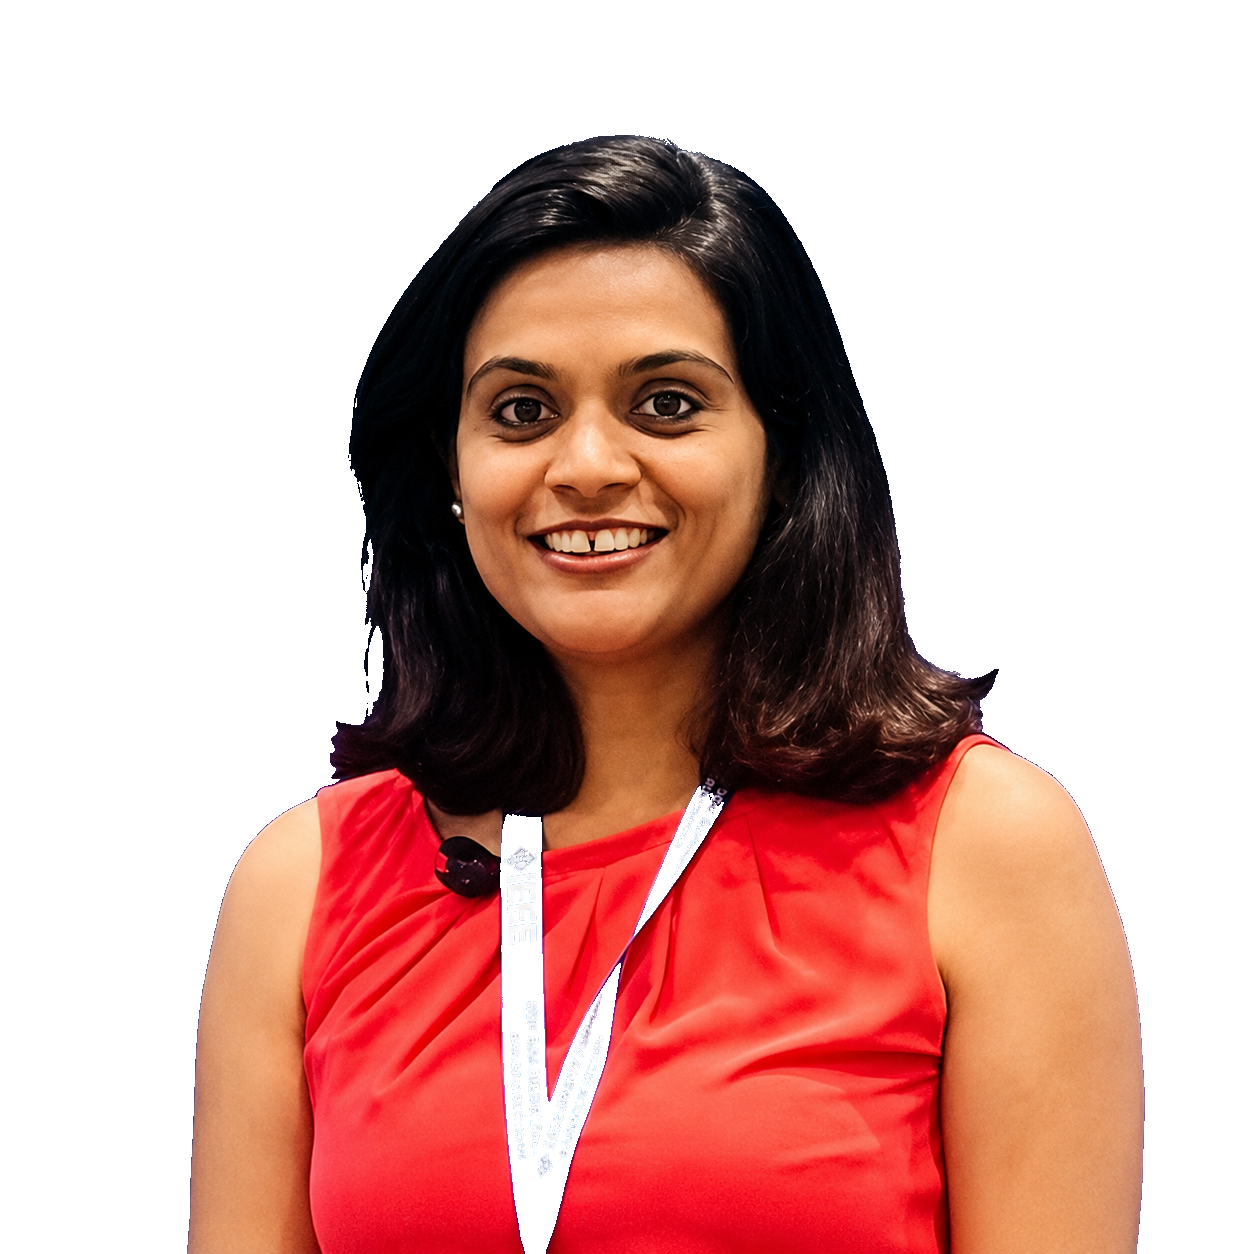
Yesha Patel
Enterprise Solution Architect
IBM
Session Details
Your AI Agent Has a Credit Card: Building Trustworthy Agentic Commerce
AI agents are quickly evolving from systems that recommend what we should do to systems that can act on our behalf—searching for products, comparing options, interacting with merchants, and potentially completing transactions. But when an AI agent can spend money, a fundamental question emerges: how much authority should we give it, and how do we know its actions truly represent the user’s intent? This session explores the trust and security architecture required for agentic commerce, where autonomous AI agents interact with commerce platforms, payment systems, customer data, and enterprise services. Through a practical shopping journey, we will examine how identity, delegated authorization, least-privilege access, scoped credentials, transaction limits, contextual risk signals, step-up approvals, and human-in-the-loop controls can help prevent an autonomous agent from becoming an uncontrolled digital actor. We will also examine failure scenarios—including manipulated instructions, excessive permissions, unintended purchases, compromised tools, and agents acting outside their authorized scope—and discuss how observability, auditability, policy enforcement, and zero-trust principles can contain their impact. Attendees will leave with a practical framework for designing AI agents that can discover, decide, and act while preserving user control, security, accountability, and trust. As AI agents move from assistants to economic actors, these safeguards will become foundational to building agentic systems people and enterprises are willing to trust.
Full conference agenda
See every session across the AI Agents Conference November 2026 line-up.
View Agenda